How to Prepare for a Penetration Test
A five-step checklist covering scope, timing, stakeholders, and rules of engagement, so your next pentest tests the right things at the right time.
Already scoped and ready to talk? Contact Us for Next Steps →
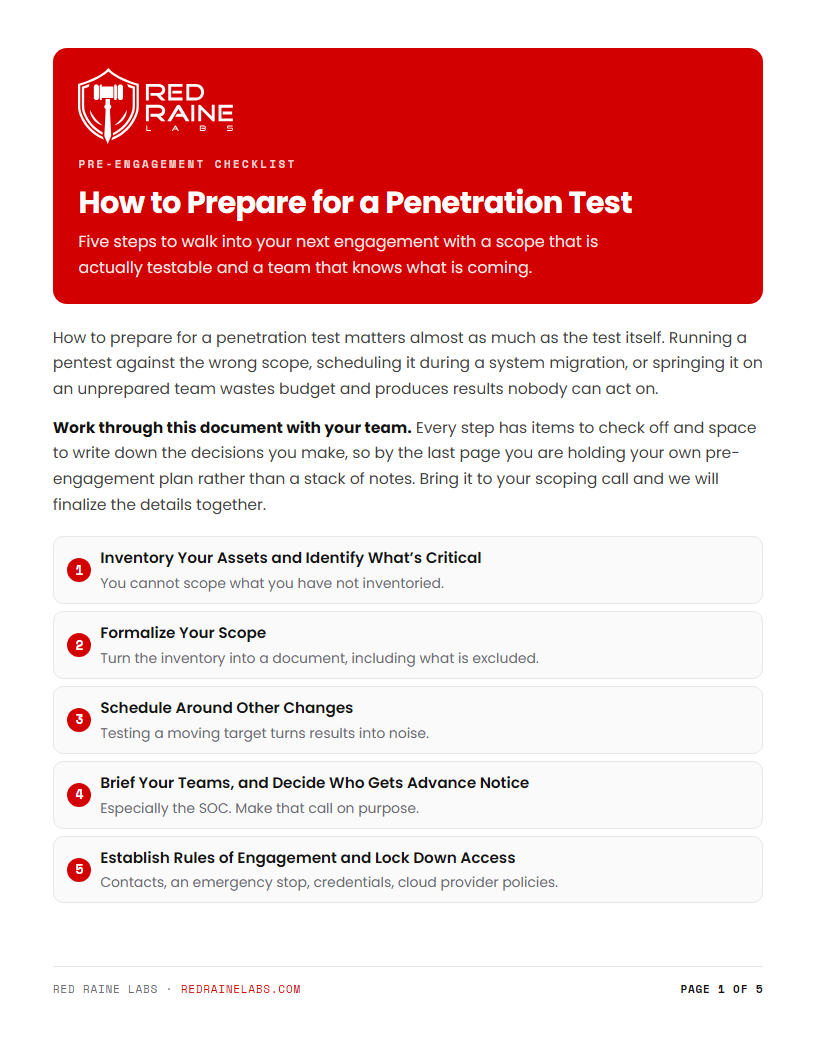
Preparation decides what you get out of the test
How to prepare for a penetration test matters almost as much as the test itself. Running a pentest against the wrong scope, scheduling it during a system migration, or springing it on an unprepared team wastes budget and produces results nobody can act on.
What’s in the checklist
We put together a free, 5-step checklist covering exactly what to do before your engagement starts. Work through it with your team and walk into your next pentest with a scope that’s actually testable and a team that knows what’s coming.
-
Inventory your assets and identify what’s critical
Servers, cloud tenants, apps, APIs, AI integrations, and which of them would hurt most if an attacker got in.
-
Formalize your scope
Turn the inventory into a document: IP ranges, domains, app URLs, tenant IDs, and what you are explicitly excluding.
-
Schedule around other IT projects
Testing during a migration or major deployment turns results into noise. Sequence the pentest after the project lands.
-
Brief your internal team and vendors
IT, security, your MSSP or MDR, and leadership, before testing begins. Then make a deliberate call on whether the SOC gets advance notice.
-
Lock down rules of engagement
Points of contact, an emergency stop procedure, the access the test actually needs, and your cloud provider’s testing policies.
Why take this from Red Raine Labs
Red Raine Labs is a Michigan-based, owner-operated penetration testing firm. Every engagement means hands-on exploitation, not automated scanning paired with a template report. We scope engagements the way this checklist describes, because a rushed or vague scope produces a report that doesn’t hold up when you need it, whether that’s for a client, an auditor, or your own leadership.
Already know which test you need?
If you already know you need an External or Internal Network Penetration Test, Web Application Penetration Test, or Cloud Penetration Test, use the checklist first, then bring your scope to a quick call and we’ll finalize it together.
Work through it, then bring us your scope
Fill in the checklist with your team and you will have everything a scoping call needs. Send it over and we will turn it into an engagement.
Download the Free ChecklistAlready scoped and ready to talk? Contact Us for Next Steps →